Tech··4 min
Cookies and consent: the CNPD checklist for auditing your Luxembourg website
In 2021 the CNPD published detailed guidelines on cookies: a reject button as visible as the accept button, consent renewed within 12 months, a legal basis to cite. Here is how to audit your banner before a possible inspection.
Translated from French · Lire l'original en français
On 6 October 2021, the Commission nationale pour la protection des données (CNPD, Luxembourg's data protection authority) published guidelines on cookies and other trackers. They apply to every website or app operator established in Luxembourg. This article is for website managers who want to check, point by point, whether their consent banner holds up before a possible inspection.
This text sets out the principles published by the CNPD for information purposes. It does not constitute legal advice and does not replace an individual analysis of your situation by a legal professional.
Why the CNPD regulates your cookie banner
The obligation to obtain the user's consent before placing non-essential cookies has a clear legal basis. It comes from Article 4.3(e) of the amended law of 30 May 2005 on the protection of privacy in the electronic communications sector, which transposes into Luxembourg law the ePrivacy Directive 2002/58/EC, itself amended by Directive 2009/136/EC, according to the coordinated text published on Legilux. In practice, as soon as a cookie is not strictly necessary to provide the service the user has requested (for example an audience measurement cookie, a targeted advertising cookie or a social media sharing cookie), placing it requires prior and informed consent. Strictly necessary cookies, such as those that run a shopping basket or a login session, are exempt from consent but must still be disclosed to the user, the CNPD specifies in its thematic dossier on cookies.
The 5-point checklist for auditing your banner
In its thematic dossier and in the PDF of its guidelines, the CNPD details the criteria it applies to assess whether a banner is compliant. Here are the five points to check first on your own website.
| Point to check | What the CNPD requires |
|---|---|
| Reject button | As visible as a “Tout accepter” (“Accept all”) button: same size, same colour, same display level |
| Two-level information | A short banner stating the purposes and the controller, linking to a detailed cookie policy |
| Distinction between cookies | Essential cookies disclosed without consent being required, non-essential cookies subject to an explicit choice |
| Renewal | Consent is valid for 12 months at most; after that, the banner must reappear |
| Legal basis | The cookie policy must cite the specific legal basis justifying the placement of each tracker |
The “tout refuser” (“reject all”) button, the most common pitfall
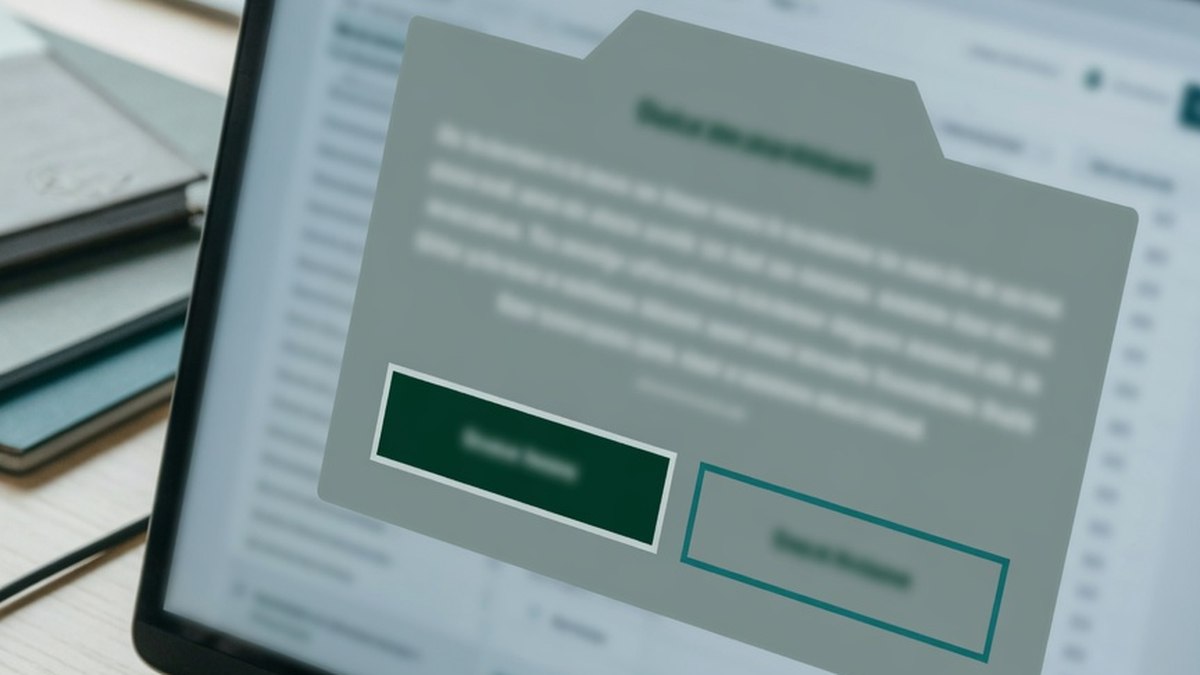
This is the point on which the CNPD is most explicit, and the one many websites still get wrong. When a banner offers a clearly visible “Tout accepter” (“Accept all”) button, a “Tout refuser” (“Reject all”) button of equivalent size, colour and position must appear at the same level, without the user having to click a secondary link or open a settings menu to find it. The CNPD describes this kind of imbalance between the two buttons as a dark pattern, a practice designed to steer the user's choice towards acceptance. If your “refuser” (“reject”) button is greyed out, smaller, or hidden on a second screen while “accepter” (“accept”) stands out in a bright colour, that is the first thing to fix.
Twelve months, no more: consent has an expiry date
Consent obtained today does not last indefinitely. The CNPD sets a maximum duration of 12 months, after which the banner must reappear to collect a new choice from the user, whether they accepted or refused the first time. Many consent management tools set this duration by default to longer values, sometimes 13 months based on foreign standards, which makes them non-compliant with Luxembourg requirements unless the setting has been adjusted manually. Checking this setting in your consent management platform (CMP) takes five minutes and avoids a gap that is easy to spot during an inspection.
Checking your banner before an inspection
The CNPD provides the full PDF of its guidelines, as well as an online thematic dossier detailing the applicable principles and how to put them into practice, including the page “Principes applicables et mise en pratique” (“Applicable principles and implementation”), which sets out the rules on the reject button and the 12-month duration. The official announcement of 6 October 2021 and the coordinated text of the law of 30 May 2005 on Legilux let you trace the requirements back to the legal basis itself. Reviewing these five points on your own website, before an inspection does it for you, remains the simplest way to limit the risk. If your website also processes personal data beyond cookies, our article on what the CNPD checks and how to prepare your company complements this checklist with an overview of GDPR obligations.